https://xelta.ai/terms-conditions
Tested 2026-10-13 07:11:29 using Chrome 150.0.7871.46 (runtime settings)
This page is fast to paint and visually stable, but a little janky to interact with, loose on best practices, weak on user privacy and slow to respond from the server.
Visual metrics
Google Web Vitals
The page is using Google Tag Manager, this is a performance risk since non-tech users can add JavaScript to your page.
The page has 9 CPU long tasks with the total of 912 ms. The total blocking time is 456 ms and 1 long task before first contentful paint with total time of 56 ms. However the CPU Long Task is depending on the computer/phones actual CPU speed, so you should measure this on the same type of the device that your user is using. Use Geckoprofiler for Firefox or Chromes tracelog to debug your long tasks.
The page has 10 requests that are missing a cache time. Configure a cache time so the browser doesn't need to download them every time. It will save 15.7 kB the next access.
Timings summary
| Metric | Min | Median | Mean | Max |
|---|---|---|---|---|
| First visual change | 1.100 s | 1.100 s | 1.100 s | 1.100 s |
| Last visual change | 5.000 s | 5.000 s | 5.000 s | 5.000 s |
| Speed index | 1.192 s | 1.192 s | 1.192 s | 1.192 s |
| Visual readiness | 3.900 s | 3.900 s | 3.900 s | 3.900 s |
| Visual complete 85 | 1.100 s | 1.100 s | 1.100 s | 1.100 s |
| Visual complete 95 | 1.633 s | 1.633 s | 1.633 s | 1.633 s |
| Visual complete 99 | 1.633 s | 1.633 s | 1.633 s | 1.633 s |
Run 1 SpeedIndex median
The red band on the timeline marks when the main thread was busy with long tasks: moments when the page could not paint or respond, however the video looks.
Download videoUse --filmstrip.showAll to show all filmstrips.
Click a frame to seek the video to that moment. The dot marks frames where the page changed visually.
The server dominated the wait. The first byte took 919 ms (84 % of the time to First Contentful Paint). Nothing can render before it arrives, and Google Web Vitals considers a TTFB over 800 ms in need of improvement. See the request timing on the Waterfall tab. First paint landed at 1.088 s; the 3 render-blocking requests were done by 985 ms and the remaining ~103 ms is style and layout work. The largest paint followed at 1.592 s.
Want to see how much CSS style-recalculation work delayed FCP and LCP, plus CPU long tasks? Run with --cpu.
Blocking requests delay both paints: the browser renders nothing until they arrive, so they push First Contentful Paint and everything after it, including the largest paint (LCP). Requests that block the parser inside the body stall everything after them in the document. Load JavaScript with defer or async, and keep non-critical CSS off the critical path with media attributes. Bars show when each request loaded on a clock that runs to the last paint (the dashed line is FCP, the clock ends at LCP); the gap after the bars is style and layout work. Web fonts are context, not blockers: text renders invisible or in a fallback face while they load, so a font finishing after a paint is the classic reason text changed late.
| Request | When it loaded | Transfer | Download |
|---|---|---|---|
document | 928 ms | 51.0 KB | 927 ms |
07zjd4lkzne2c.cssblocking | 44 ms | 98.3 KB | 44 ms |
2951_j97le6r5.cssblocking | 41 ms | 908 B | 41 ms |
2y7vqocokaqma.cssblocking | 32 ms | 1.1 KB | 32 ms |
email-decode.min.jsblocks parser in body | 29 ms | 913 B | 29 ms |
1fzdumdazi_zk.jspotentially blocking | 143 ms | 73.3 KB | 143 ms |
1qeqbdqs6aw5_.jspotentially blocking | 139 ms | 48.9 KB | 139 ms |
3syn4ku7n9yd8.jspotentially blocking | 135 ms | 15.2 KB | 135 ms |
1rttzs2jjmcrm.jspotentially blocking | 131 ms | 44.0 KB | 131 ms |
| 22 more requests | all done by 1.143 s | 212.3 KB | |
54 ms | 65.6 KB | 54 ms | |
36 ms | 8.9 KB | 36 ms | |
34 ms | 8.8 KB | 34 ms | |
0398 ms796 msFCP 1.088 sLCP 1.592 s |
The coach helps you find performance problems on your web page using web performance best practice rules. And gives you advice on privacy and best practices. Tested using Coach-core version 9.2.1.
googleTagManagerThe page is using Google Tag Manager, this is a performance risk since non-tech users can add JavaScript to your page.
Google Tag Manager makes it possible for non tech users to add scripts to your page that will downgrade performance.
longTasksThe page has 9 CPU long tasks with the total of 912 ms. The total blocking time is 456 ms and 1 long task before first contentful paint with total time of 56 ms. However the CPU Long Task is depending on the computer/phones actual CPU speed, so you should measure this on the same type of the device that your user is using. Use Geckoprofiler for Firefox or Chromes tracelog to debug your long tasks.
Long CPU tasks locks the thread. To the user this is commonly visible as a "locked up" page where the browser is unable to respond to user input; this is a major source of bad user experience on the web today. However the CPU Long Task is depending on the computer/phones actual CPU speed, so you should measure this on the same type of the device that your user is using. To debug you should use the Chrome timeline log and drag/drop it into devtools or use Firefox Geckoprofiler.
cacheHeadersThe page has 10 requests that are missing a cache time. Configure a cache time so the browser doesn't need to download them every time. It will save 15.7 kB the next access.
The easiest way to make your page fast is to avoid doing requests to the server. Setting a cache header on your server response will tell the browser that it doesn't need to download the asset again during the configured cache time! Always try to set a cache time if the content doesn't change for every request.
javascriptSizeThe total JavaScript transfer size is 1.4 MB and the uncompressed size is 4.2 MB. This is totally crazy! There is really room for improvement here.
A lot of JavaScript often means you are downloading more than you need. How complex is the page and what can the user do on the page? Do you use multiple JavaScript frameworks?
avoidScalingImagesThe page has 8 images that are scaled more than 100 pixels. It would be better if those images are sent so the browser don't need to scale them.
It's easy to scale images in the browser and make sure they look good in different devices, however that is bad for performance! Scaling images in the browser takes extra CPU time and will hurt performance on mobile. And the user will download extra kilobytes (sometimes megabytes) of data that could be avoided. Don't do that, make sure you create multiple version of the same image server-side and serve the appropriate one.
cssSizeThe total CSS transfer size is 102.7 kB and uncompressed size is 746.2 kB. That is big and the CSS could most probably be smaller.
Delivering a massive amount of CSS to the browser is not the best thing you can do, because it means more work for the browser when parsing the CSS against the HTML and that makes the rendering slower. Try to send only the CSS that is used on that page. And make sure to remove CSS rules when they aren't used anymore.
| URL | Transfer | Content |
|---|---|---|
| https://xelta.ai/_next/static/chunks/07zjd4lkzne2c.css | 98.3 KB | 720.0 KB |
| https://xelta.ai/_next/static/chunks/2y7vqocokaqma.css | 1.1 KB | 6.4 KB |
| https://xelta.ai/_next/static/chunks/2951_j97le6r5.css | 908 B | 2.3 KB |
fewFontsThe page has 5 font requests. Do you really need them? What value does the fonts give the user?
How many fonts do you need on a page for the user to get the message? Fonts can slow down the rendering of content, try to avoid loading too many of them because worst case it can make the text invisible until they are loaded (FOIT—flash of invisible text), best case they will flicker the text content when they arrive.
privateAssetsThe page has 4 requests with private headers. The main page has a private header. It could be right in some cases where the user can be logged in and served specific content. But if your asset is static it should never be private. Make sure that the assets really should be private and only used by one user. Otherwise, make it cacheable for everyone.
If you set private headers on content, that means that the content are specific for that user. Static content should be able to be cached and used by everyone. Avoid setting the cache header to private.
cacheHeadersLongThe page has 14 requests that have a shorter cache time than one year (but still a cache time).
Setting a cache header is good. Setting a long cache header (a year) is even better because the asset will stay in the browser cache across visits. For content-hashed URLs (e.g. app.4af2.css) you can safely use Cache-Control: max-age=31536000, immutable. For unversioned URLs that may change, use a revalidating strategy instead.
optimalCssSizehttps://xelta.ai/_next/static/chunks/07zjd4lkzne2c.css size is 100.7 kB (100657) and that is bigger than the limit of 25 kB. Try to keep each CSS response under 25 kB.
Render-blocking CSS holds up the first paint until it has fully downloaded, parsed and applied, so smaller CSS files mean a faster start. Split your CSS into a small critical bundle inlined or eagerly loaded, with the rest lazy-loaded.
| URL | Transfer | Content |
|---|---|---|
| https://xelta.ai/_next/static/chunks/07zjd4lkzne2c.css | 98.3 KB | 720.0 KB |
inlineCssThe page has both inline CSS and CSS requests even though it uses a HTTP/2-ish connection. If you have many users on slow connections, it can be better to only inline the CSS. Run your own tests and check the waterfall graph to see what happens.
In the early days of the Internet, inlining CSS was one of the ugliest things you can do. That has changed if you want your page to start rendering fast for your user. Always inline the critical CSS when you use HTTP/1 and HTTP/2 (avoid doing CSS requests that block rendering) and lazy load and cache the rest of the CSS. It is a little more complicated when using HTTP/2. Does your server support HTTP push? Then maybe that can help. Do you have a lot of users on a slow connection and are serving large chunks of HTML? Then it could be better to use the inline technique, becasue some servers always prioritize HTML content over CSS so the user needs to download the HTML first, before the CSS is downloaded.
mimeTypesThe page has 1 misconfigured mime type.
It's not a great idea to let browsers guess content types (content sniffing), in some cases it can actually be a security risk.
unnecessaryHeadersThere are 1 response that sets a p3p header. There are 4 responses that sets both a max-age and expires header. There are 3 responses that sets a pragma no-cache header (that is a request header). There are 95 responses that sets a server header.
Do not send headers that you don't need. We look for p3p, cache-control and max-age, pragma, server and x-frame-options headers. Have a look at Andrew Betts - Headers for Hackers talk as a guide https://www.youtube.com/watch?v=k92ZbrY815c or read https://www.fastly.com/blog/headers-we-dont-want.
pageTitleThe title is too long by 1 characters. The recommended max is 60
Use a title to make the page more relevant to search engines.
thirdPartyThe page do 11% requests to third party domains (11 requests and 607.3 kB). First party is 86 requests and 1.2 MB. The regex .*xelta.* was used to calculate first/third party requests.
Do not load most of your content from third party URLs.
longHeadershttps://xelta.ai/cdn-cgi/speculation has a header report-to that is 606 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header content-security-policy-report-only that is 805 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header report-to that is 605 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header content-security-policy-report-only that is 805 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header report-to that is 603 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header content-security-policy-report-only that is 805 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header report-to that is 609 characters long. https://xelta.ai/_ne...7m9ogm38dql.woff2 has a header content-security-policy-report-only that is 804 characters long. https://xelta.ai/_ne...7m9ogm38dql.woff2 has a header report-to that is 608 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header content-security-policy-report-only that is 805 characters long. https://xelta.ai/_ne...ta.ai/_next/image has a header report-to that is 607 characters long. https://connect.face...en_US/fbevents.js has a header content-security-policy that is 1344 characters long. https://connect.face...en_US/fbevents.js has a header permissions-policy that is 874 characters long. https://connect.face.../1123404090023729 has a header content-security-policy that is 1344 characters long. https://connect.face.../1123404090023729 has a header permissions-policy that is 874 characters long.
Do not send response headers that are too long.
manyHeadershttps://xelta.ai/api...nt/public/pricing has 33 headers.https://xelta.ai/api/cms/maintenance has 33 headers.https://xelta.ai/api...cms/notifications has 33 headers.https://xelta.ai/api...nts/active-banner has 33 headers.https://xelta.ai/api...cms/announcements has 33 headers.https://xelta.ai/api...api/page-metadata has 31 headers.https://xelta.ai/api/geo has 32 headers.
Avoid send too many response headers.
gaThe page is using Google Analytics meaning you share your users private information with Google. You should use analytics that care about user privacy, something like https://matomo.org.
Google Analytics share private user information with Google that your user hasn't agreed on sharing.
surveillanceThe page embeds 4 resources from companies that profit from user surveillance. Consider privacy-respecting alternatives.
Embedding scripts or iframes from companies whose business model is surveillance capitalism (Google, Facebook, etc.) leaks detailed user data on every page view, often before the user has had a chance to consent. See https://en.wikipedia.org/wiki/Surveillance_capitalism for background. Prefer privacy-respecting alternatives where possible.
crossOriginEmbedderPolicyHeaderSet a Cross-Origin-Embedder-Policy header (typically require-corp or credentialless) on the document response to control cross-origin embedding.
Cross-Origin-Embedder-Policy (COEP) makes the page refuse to load cross-origin subresources unless they explicitly opt in via CORP or CORS. Together with Cross-Origin-Opener-Policy it puts the page in a cross-origin isolated context, which mitigates cross-window side-channel attacks (Spectre) and unlocks high-resolution timers and SharedArrayBuffer. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Embedder-Policy
crossOriginOpenerPolicyHeaderSet a Cross-Origin-Opener-Policy header (typically same-origin) on the document response to isolate the page from cross-origin windows.
Cross-Origin-Opener-Policy (COOP) lets a page sever its window-group ties to cross-origin documents that opened it or that it opens. Together with Cross-Origin-Embedder-Policy it puts the page in a cross-origin isolated context, which mitigates cross-window side-channel attacks (Spectre) and unlocks high-resolution timers and SharedArrayBuffer. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Opener-Policy
crossOriginResourcePolicyHeaderSet a Cross-Origin-Resource-Policy header (same-origin, same-site or cross-origin) on the document response to limit who may embed it.
Cross-Origin-Resource-Policy (CORP) is a per-response opt-in that tells the browser which origins are allowed to embed the resource. It blocks cross-origin or cross-site no-cors embedding (img, script, iframe, etc.) and is one of the building blocks of cross-origin isolation. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Resource-Policy
thirdPartyPrivacyThe page has 8% requests that are 3rd party (8 requests with a size of 606.7 kB). The page also have request to companies that harvest data from users and do not respect users privacy (see https://en.wikipedia.org/wiki/Surveillance_capitalism). The page do 2 utility requests and uses 2 utility tools. The page do 2 social requests and uses 1 social tool. The page do 7 survelliance requests and uses 5 survelliance tools. The page do 7 surveillance requests and uses 5 surveillance tools. The page do 2 tag-manager requests and uses 1 tag-manager tool. The page do 1 analytics request and uses 1 analytics tool. The page do 1 ad request and uses 1 ad tool.
Using third party requests shares user information with that third party. Please avoid that! The project https://github.com/patrickhulce/third-party-web is used to categorize first/third party requests.
contentSecurityPolicyHeaderThe policy allows 'unsafe-inline', which lets the browser execute inline scripts and styles directly from the page. Move to nonces or hashes plus 'strict-dynamic' so that inline injection cannot run.
A Content-Security-Policy response header tells the browser which sources of script, style, and other content are allowed. The most effective form is a strict CSP using nonces or hashes together with strict-dynamic; the worst is a missing header, with unsafe-inline and unsafe-eval close behind. https://web.dev/articles/strict-csp
A snapshot of what the browser actually built for this page: the document, how big and deep the DOM tree is and what it kept in storage. Big, deep trees are slower to style and lay out, so the counts Chrome warns about carry a flag.
Document
What the page says it is and how large it rendered.
DOM structure
How much markup the browser has to build, style and lay out.
Storage and connection
What the page stored on the client, and the network it was tested on.
Data collected using
Coach-core version 9.2.1. With updated code from
Webappanalyzer 2026-05-04. Use
--browsertime.firefox.includeResponseBodies html or
--browsertime.chrome.includeResponseBodies html to help Wappalyzer find more information about technologies used.
Data collected using Third Party Web version 0.29.2.
Data from run 1
0.0s1.5s1.9s2.3s2.6s3.0s3.4s5.0sWhen the page main content is rendered, collected via the Largest Contentful Paint API. Read more about Largest Contentful Paint.
body > div#app-root > section > div > div > div > div > div > div > div:eq(1) > p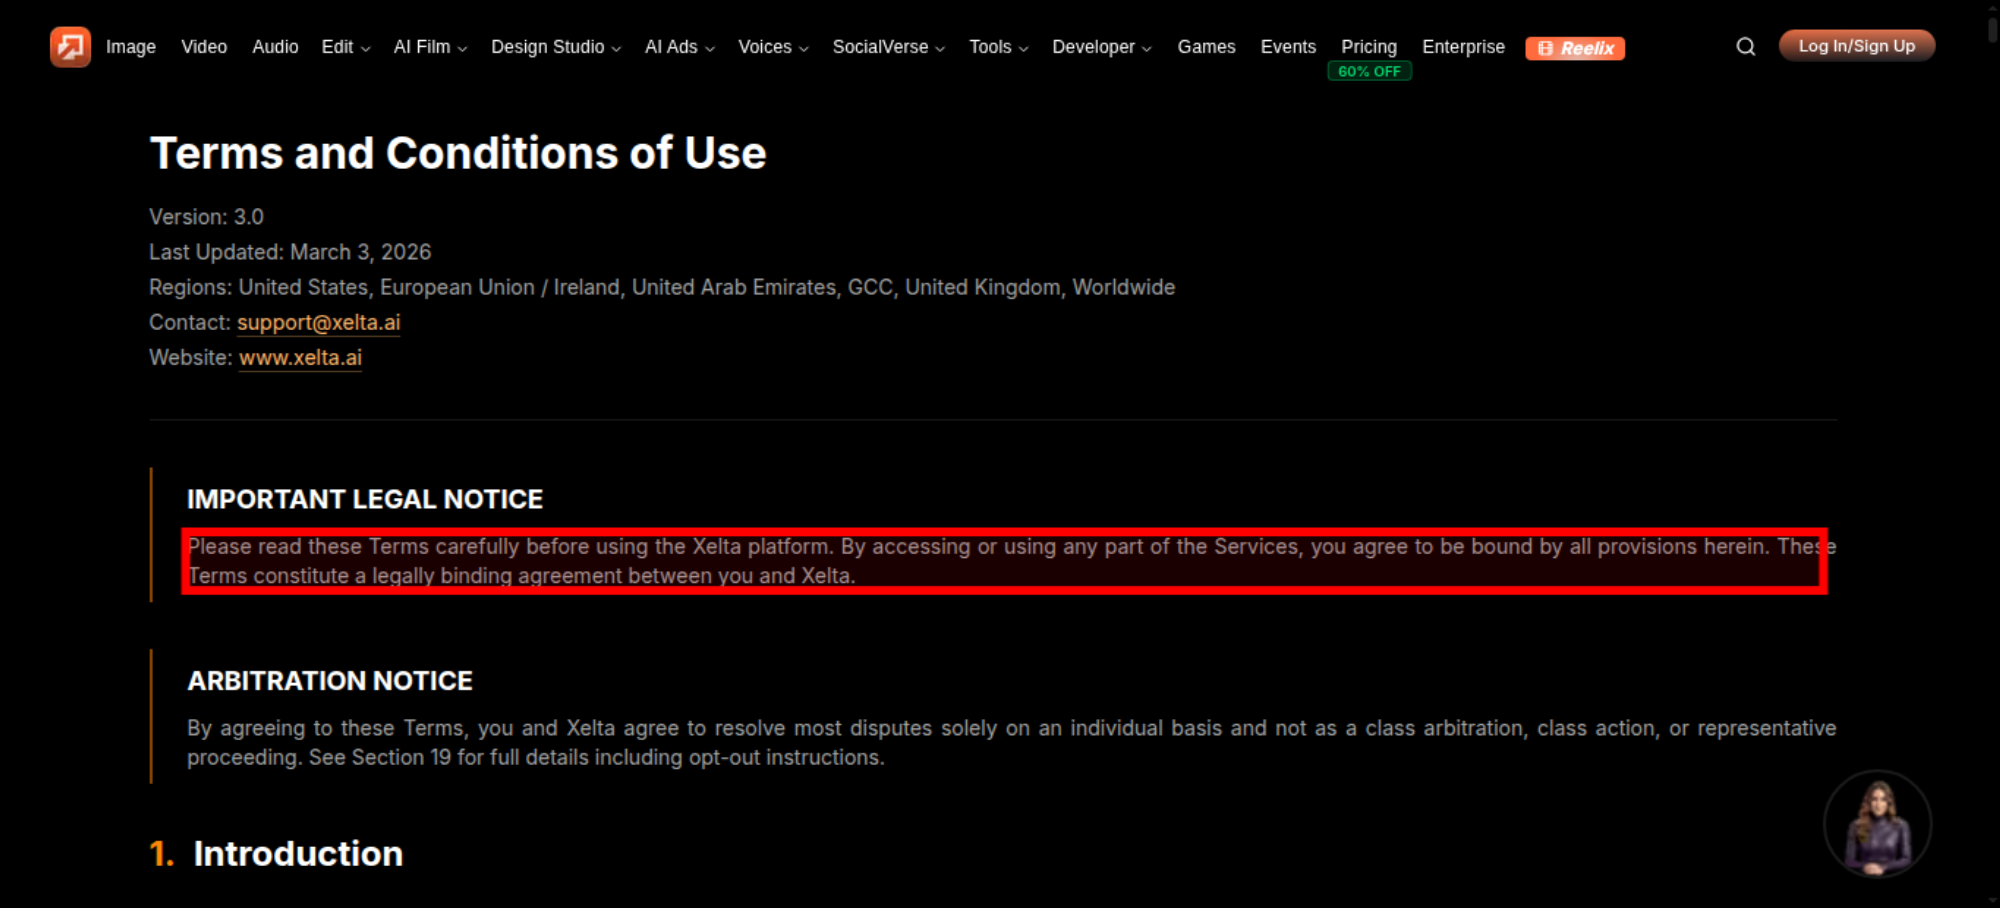
The LCP element is highlighted in the screenshot. If nothing is highlighted the element was removed before the screenshot or the LCP API couldn't find it.
How much the page's content shifts as it loads, collected via the Cumulative Layout Shift API.
Sorted by individual shift score (higher = bigger shift). The top entries usually account for most of the page's CLS.
body > div#app-root > header > div > div:eq(2)
Elements that shifted by more than 0.01 are highlighted in the screenshot. If an element shifted outside the viewport, it won't appear here. Check the video or filmstrip to see the shift.
Timing data the server chose to expose through Server-Timing response headers on the main document — typically backend time, cache status or experiment flags.
| Name | Duration | Description |
|---|---|---|
cfCacheStatus | 0 ms | DYNAMIC |
cfEdge | 11 ms | – |
cfOrigin | 913 ms | – |
There are no custom configured scripts.
There are no custom extra metrics from scripting.
How the page is built.
https://xelta.ai/terms-conditions
| Header | Value |
|---|---|
alt-svc | h3=":443"; ma=86400 |
cache-control | private, no-cache, no-store, max-age=0, must-revalidate |
cf-cache-status | DYNAMIC |
cf-ray | a49c87e4a8dca769-DEL |
content-encoding | br |
content-security-policy | default-src 'self'; script-src 'self' 'unsafe-inline' https:; style-src 'self' 'unsafe-inline' https://fonts.googleapis.com; font-src 'self' https://fonts.gstatic.com data:; img-src 'self' data: blob: https:; media-src 'self' https: blob:; connect-src 'self' https: wss: blob:; worker-src 'self' blob:; frame-src 'self' https:; frame-ancestors 'none'; object-src 'none'; base-uri 'self'; form-action 'self' https://www.facebook.com |
content-security-policy-report-only | default-src 'self'; script-src 'self' 'unsafe-inline' 'unsafe-eval' https:; style-src 'self' 'unsafe-inline' https:; img-src 'self' data: blob: https:; font-src 'self' data: https:; media-src 'self' data: blob: https:; connect-src 'self' https: wss: blob:; worker-src 'self' blob:; frame-src 'self' https:; object-src 'none'; base-uri 'self'; form-action 'self' https:; frame-ancestors 'self'; |
content-type | text/html; charset=utf-8 |
date | Tue, 13 Oct 2026 07:11:33 GMT |
expect-ct | max-age=86400, enforce |
link | </_next/static/media/inter_latin_wght-s.p.2bn3s6zvc0dyp.woff2>; rel=preload; as="font"; crossorigin=""; type="font/woff2" |
nel | {"report_to":"cf-nel","success_fraction":0.0,"max_age":604800} |
permissions-policy | camera=(), microphone=(self), geolocation=(), interest-cohort=() |
referrer-policy | same-origin strict-origin-when-cross-origin |
report-to | {"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=TgVa%2FEB4aayFJ7vBUuTIOuzyOxQJo10Y71jJ%2BzFUaE3EJuWMcEz%2FV2o33td5sBJ9aqRXFR%2BYaSFDf5AeMsMHjbwBn9HBOXnnZHGCDbianvNh0CH1b2yZTc8L"}]} |
server | cloudflare |
server-timing | cfCacheStatus;desc="DYNAMIC" cfEdge;dur=11,cfOrigin;dur=913 |
speculation-rules | "/cdn-cgi/speculation" |
strict-transport-security | max-age=31536000; includeSubDomains; preload |
vary | rsc, next-router-state-tree, next-router-prefetch, next-router-segment-prefetch, Accept-Encoding |
x-content-type-options | nosniff |
x-frame-options | SAMEORIGIN |
x-xss-protection | 1; mode=block |
Transfer size1.7 MB
Content size5.4 MB
Requests97
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 51.0 KB | 403.1 KB | 1 |
| css | 0 b | 100.3 KB | 728.7 KB | 3 |
| javascript | 0 b | 1.3 MB | 4.0 MB | 60 |
| image | 0 b | 116.7 KB | 100.3 KB | 12 |
| font | 0 b | 141.1 KB | 134.9 KB | 5 |
| favicon | 0 b | 9.6 KB | 8.3 KB | 1 |
| other | 0 b | 1.3 KB | 151 B | 1 |
| json | 0 b | 14.8 KB | 4.6 KB | 9 |
| plain | 0 b | 1.4 KB | 2 B | 5 |
| Total | 0 b | 1.7 MB | 5.4 MB | 97 |
| Domain | Total download time | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| xelta.ai | 10.802 s | 1.1 MB | 3.5 MB | 86 |
| static.cloudflareinsights.com | 93 ms | 10.2 KB | 30.9 KB | 1 |
| us.i.posthog.com | 1.102 s | 286 B | 15 B | 1 |
| telemetry.matchbestsoftware.online | 179 ms | 286 B | 2 B | 2 |
| connect.facebook.net | 390 ms | 274.3 KB | 990.5 KB | 2 |
| www.googletagmanager.com | 661 ms | 307.0 KB | 902.1 KB | 2 |
| analytics.google.com | 162 ms | N/A | 0 b | 1 |
| stats.g.doubleclick.net | 120 ms | 553 B | 0 b | 1 |
| www.google.co.in | 125 ms | 408 B | 42 B | 1 |
| type | min | median | max |
|---|---|---|---|
| Expires | 0 seconds | 1 year | 1 year |
| Last modified | 1 hour | 2 days | 1 week |
Includes requests done after load event end.
| Content | Transfer Size | Requests |
|---|---|---|
| html | 0 b | 0 |
| css | 0 b | 0 |
| javascript | 916.3 KB | 31 |
| image | 9.4 KB | 3 |
| font | 92.7 KB | 4 |
| favicon | 9.6 KB | 1 |
| plain | 1.4 KB | 5 |
| json | 12.8 KB | 8 |
| Total | 1.0 MB | 52 |
Includes requests done after DOM content loaded.
| Content | Transfer Size | Requests |
|---|---|---|
| html | 0 b | 0 |
| css | 0 b | 0 |
| javascript | 916.3 KB | 31 |
| image | 9.4 KB | 3 |
| font | 92.7 KB | 4 |
| favicon | 9.6 KB | 1 |
| plain | 1.4 KB | 5 |
| json | 12.8 KB | 8 |
| Total | 1.0 MB | 52 |
--enableProfileRun to see where main-thread time went, blocking time and CPU cost per script, module and function, forced reflows and frame stability. The data is collected in one extra run, so the timing metrics of your measured runs stay untouched.Tasks ≥ 50 ms blocking the main thread, collected via the Long Task API.
A long animation frame (LOAF) is a frame that took ≥ 50 ms from input to the next paint. The part beyond the threshold is blocking time, the number that hurts Interaction to Next Paint and Total Blocking Time. Break long tasks up (scheduler.yield(), smaller chunks) or move the work off the main thread. Read more about the Long Animation Frames API.
| Script | Frames | Time running | Blocking (share by run time) | Forced style & layout | Triggered by |
|---|---|---|---|---|---|
| fbevents.js3rd party | 1 | 235.6 ms | 185.6 ms | – | script tag |
| 1fzdumdazi_zk.js | 2 | 138.8 ms | 100.4 ms | – | event handler, timer or animation callback |
| 11234040900237293rd party | 1 | 131.8 ms | 81.7 ms | – | script tag |
| js3rd party | 1 | 91 ms | 41.1 ms | – | script tag |
| gtm.js3rd party | 1 | 80.2 ms | 30.3 ms | – | script tag |
| 32w4p10g8-c72.js | 1 | 26.7 ms | 8.8 ms | – | script tag |
| 0ydxpfwuv6kde.js | 1 | 6.8 ms | 2.2 ms | – | script tag |
| TimerHandler:setTimeout | 1 | 51.5 ms | 1.9 ms | – | timer or animation callback |
A frame's blocking time is split between its scripts by their share of the frame's work, capped at each script's own run time — blocking from work no script owns (HTML parsing, browser internals) stays unattributed. The per-script blocking view below uses the same attribution.
The browser did not report which script was responsible for this frame — typically its own style/layout work, or a cross-origin script it will not name.
How much each script blocked the main thread, derived from the Long Animation Frame API. Each frame's blocking time is split between its scripts by their share of the frame's work, capped at each script's own run time — blocking from work no script owns (HTML parsing, browser internals) is not attributed (older data credits the script that started the frame). The closest answer to "which script should I fix to improve TBT" the platform exposes.
Third party requests categorised by Third party web version 0.29.2.
Requests by category15
Domains that didn't match any tool in Third party web. If you are sure they are third party domains, please do a PR to that project. You can also fine tune the list using --firstParty.
Transfer size1.7 MB
Content size5.4 MB
Requests97
Calculated using .*xelta.* (use --firstParty to configure).
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 51.0 KB | 403.1 KB | 1 |
| css | 0 b | 100.3 KB | 728.7 KB | 3 |
| javascript | 0 b | 733.2 KB | 2.1 MB | 55 |
| image | 0 b | 116.3 KB | 100.2 KB | 11 |
| font | 0 b | 141.1 KB | 134.9 KB | 5 |
| favicon | 0 b | 9.6 KB | 8.3 KB | 1 |
| other | 0 b | 1.3 KB | 151 B | 1 |
| json | 0 b | 14.5 KB | 4.6 KB | 8 |
| plain | 0 b | 571 B | 0 b | 1 |
| Total | N/A | 1.1 MB | 3.5 MB | 86 |
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 0 b | 0 b | 0 |
| css | 0 b | 0 b | 0 b | 0 |
| javascript | 0 b | 591.6 KB | 1.9 MB | 5 |
| image | 0 b | 408 B | 42 B | 1 |
| font | 0 b | 0 b | 0 b | 0 |
| favicon | 0 b | 0 b | 0 b | 0 |
| json | 0 b | 286 B | 15 B | 1 |
| plain | 0 b | 839 B | 2 B | 4 |
| Total | N/A | 593.1 KB | 1.9 MB | 11 |