Tested 2026-09-04 07:39:21 using Chrome 150.0.7871.46 (runtime settings)
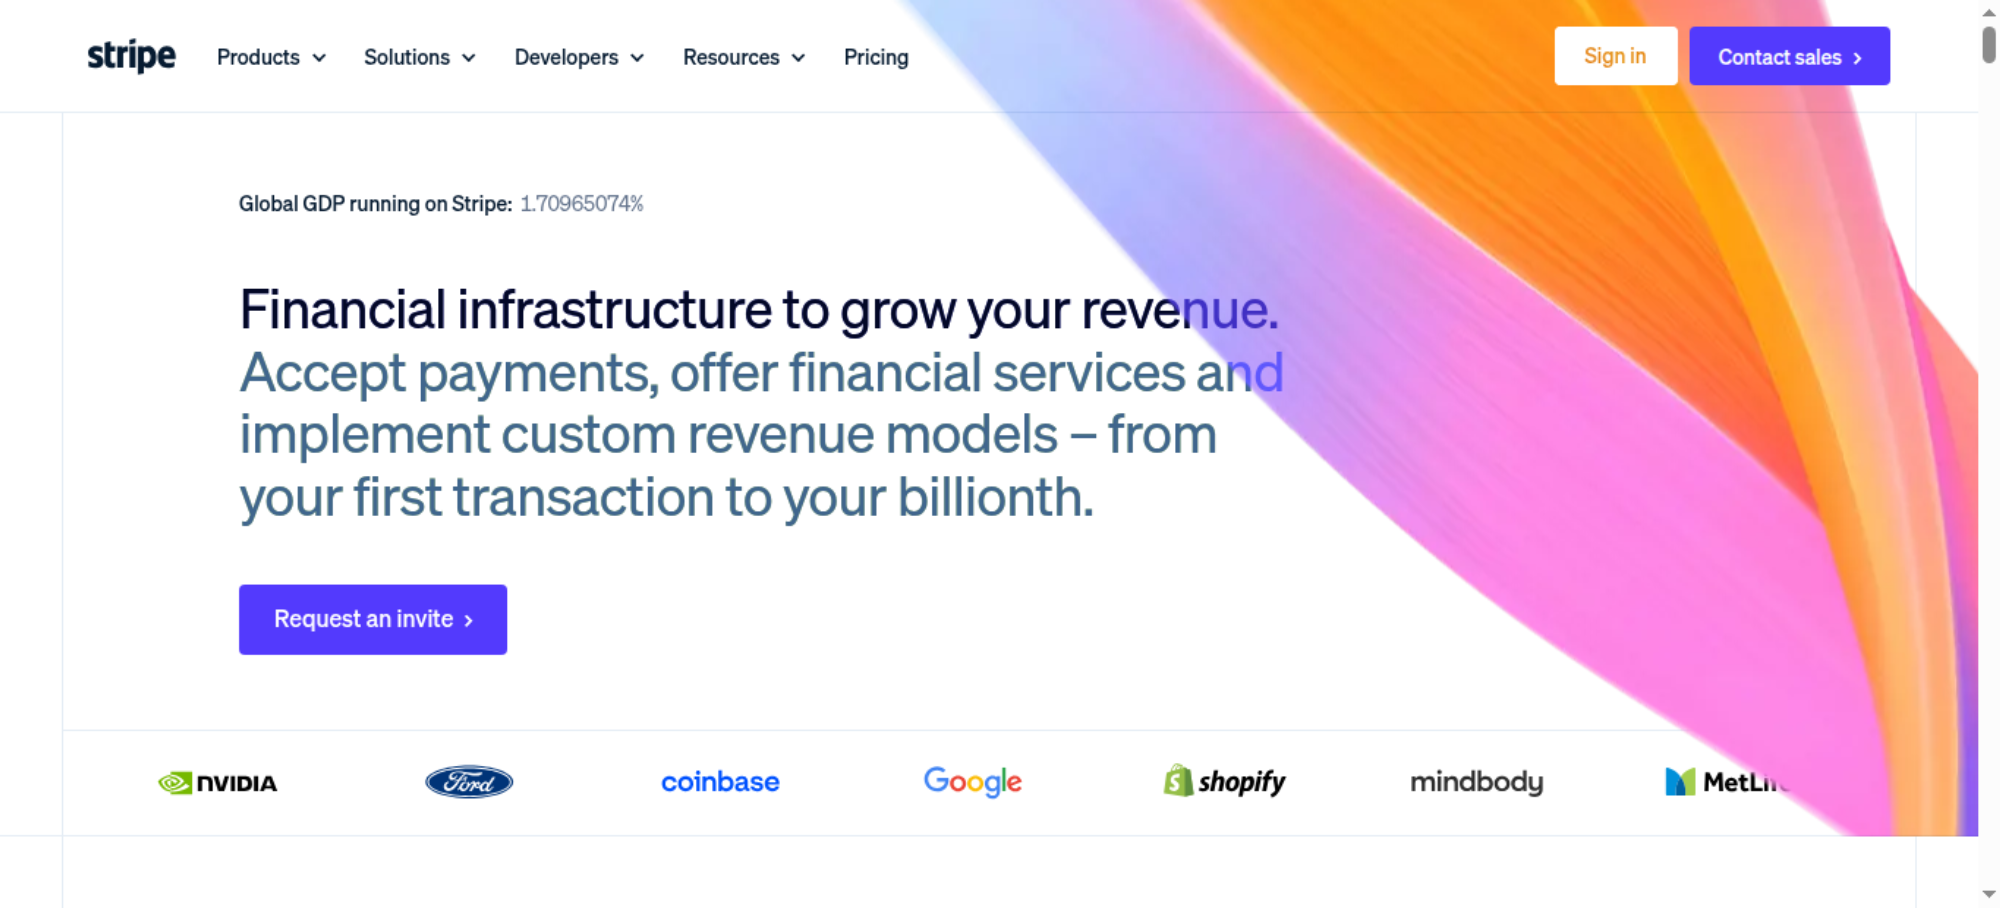
The red band on the timeline marks when the main thread was busy with long tasks: moments when the page could not paint or respond, however the video looks.
Download videoUse --filmstrip.showAll to show all filmstrips.
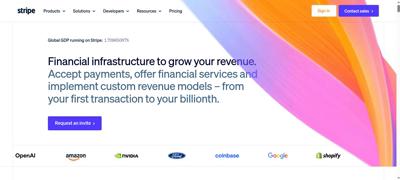
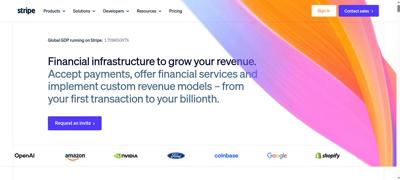
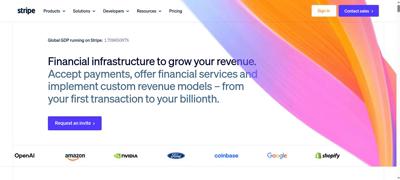
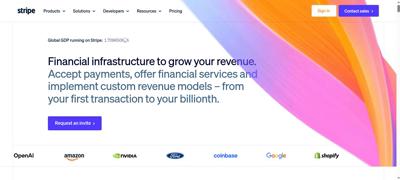
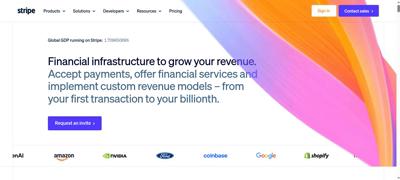
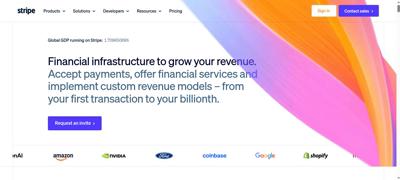
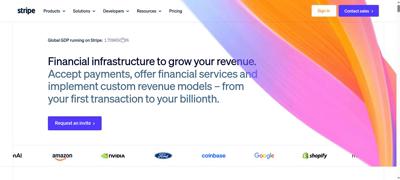
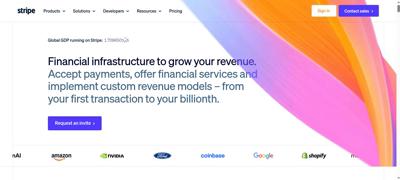
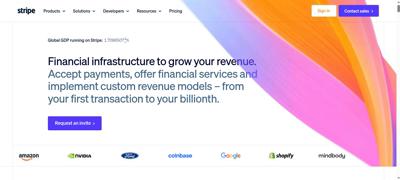
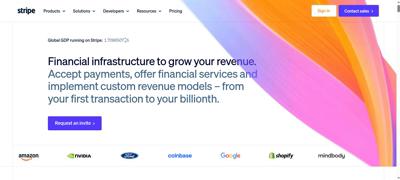
Click a frame to seek the video to that moment. The dot marks frames where the page changed visually.
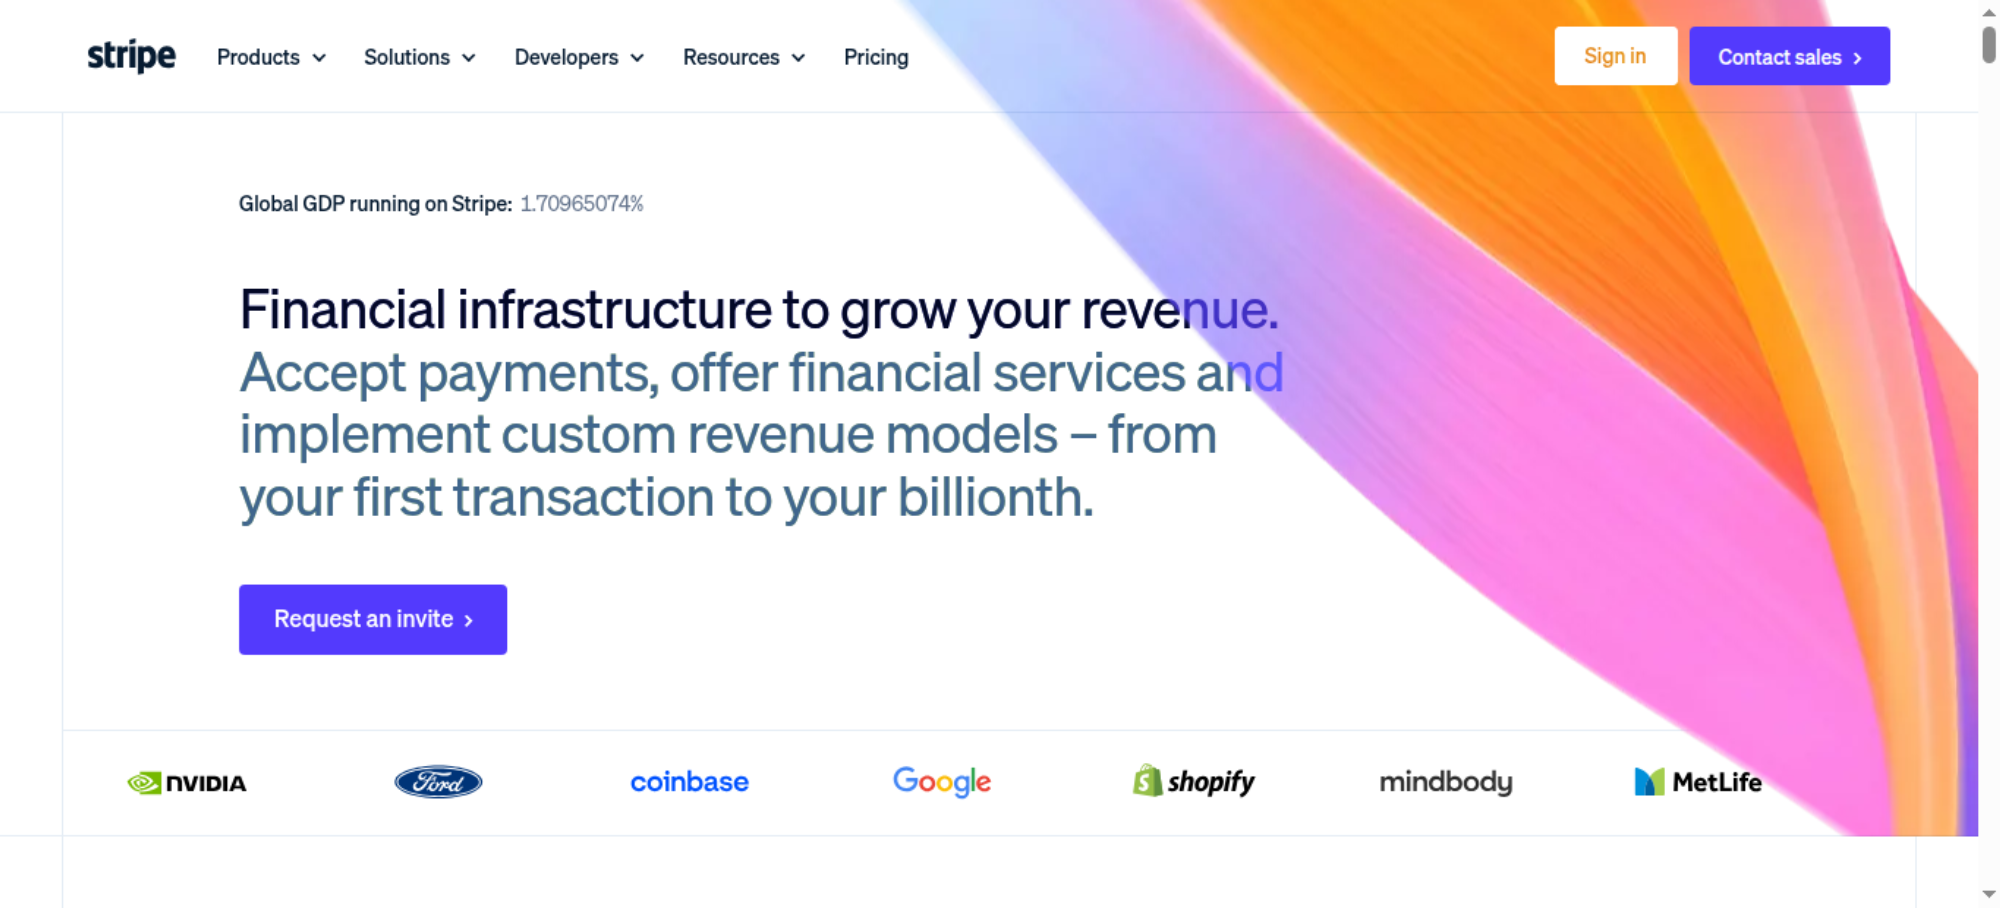
The server dominated the wait. The first byte took 1.539 s (66 % of the time to First Contentful Paint). Nothing can render before it arrives, and Google Web Vitals considers a TTFB over 800 ms in need of improvement. See the request timing on the Waterfall tab. First paint landed at 2.324 s.
Want to see how much CSS style-recalculation work delayed FCP and LCP, plus CPU long tasks? Run with --cpu.
Blocking requests delay both paints: the browser renders nothing until they arrive, so they push First Contentful Paint and everything after it, including the largest paint (LCP). Requests that block the parser inside the body stall everything after them in the document. Load JavaScript with defer or async, and keep non-critical CSS off the critical path with media attributes. Bars show when each request loaded on a clock that runs to the last paint; the gap after the bars is style and layout work. Web fonts are context, not blockers: text renders invisible or in a fallback face while they load, so a font finishing after a paint is the classic reason text changed late.
| Request | When it loaded | Transfer | Download |
|---|---|---|---|
document | 847 ms | 259 B | 844 ms |
PrivacyCompliance.2a784d61fe051092c5dd.bundle.jsblocks parser in body | loaded after FCP, at 3.880 s | 3.4 KB | 46 ms |
PrivacyCompliance.2a784d61fe051092c5dd.bundle.jsblocks parser in body | loaded after FCP, at 3.888 s | 0 b | 43 ms |
loaded after FCP, at 3.888 s | 0 b | 42 ms | |
loaded after FCP, at 3.879 s | 22.9 KB | 42 ms | |
GoogleTagManager.d1238f0d2797867a533d.bundle.jsblocks parser in body | loaded after FCP, at 4.804 s | 3.6 KB | 19 ms |
GoogleTagManager.d1238f0d2797867a533d.bundle.jsblocks parser in body | loaded after FCP, at 4.817 s | 0 b | 8 ms |
LCP resource | 176 ms | 33.1 KB | 176 ms |
230 ms | 58.1 KB | 230 ms | |
183 ms | 12.1 KB | 183 ms | |
0581 ms1.162 sFCP · LCP 2.324 s |
The coach helps you find performance problems on your web page using web performance best practice rules. And gives you advice on privacy and best practices. Tested using Coach-core version 9.2.1.
decodingAsyncThe page has 40 images (out of 40) without a decoding hint. Add decoding="async" to non-critical images so the browser can decode them off the main thread.
Setting decoding="async" on an <img> tells the browser it can decode the image off the main thread, which keeps the page responsive to user interactions while images are being processed. The default ("auto") leaves the choice to the browser. https://developer.mozilla.org/en-US/docs/Web/HTML/Element/img#decoding
longTasksThe page has 16 CPU long tasks with the total of 3.142 s. The total blocking time is 2.091 s and 3 long tasks before first contentful paint with total time of 401 ms. However the CPU Long Task is depending on the computer/phones actual CPU speed, so you should measure this on the same type of the device that your user is using. Use Geckoprofiler for Firefox or Chromes tracelog to debug your long tasks.
Long CPU tasks locks the thread. To the user this is commonly visible as a "locked up" page where the browser is unable to respond to user input; this is a major source of bad user experience on the web today. However the CPU Long Task is depending on the computer/phones actual CPU speed, so you should measure this on the same type of the device that your user is using. To debug you should use the Chrome timeline log and drag/drop it into devtools or use Firefox Geckoprofiler.
assetsRedirectsThe page has 14 redirects. 2 of the redirects are from the base domain, please fix them! 12 requests are from other domains, it could be 3rd-party assets doing unnecessary redirects. :(
A redirect is one extra step for the user to download the asset. Avoid that if you want to be fast. Redirects are even more of a showstopper on mobile.
cacheHeadersThe page has 41 requests that are missing a cache time. Configure a cache time so the browser doesn't need to download them every time. It will save 67.8 kB the next access.
The easiest way to make your page fast is to avoid doing requests to the server. Setting a cache header on your server response will tell the browser that it doesn't need to download the asset again during the configured cache time! Always try to set a cache time if the content doesn't change for every request.
documentRedirectThe main document gets redirected 2 time(s). Remove those redirect and make the page faster!
You should never ever redirect the main document, because it will make the page load slower for the user. Well, you should redirect the user if the user tries to use HTTP and there's an HTTPS version of the page. The coach checks for that. :)
javascriptSizeThe total JavaScript transfer size is 2.2 MB and the uncompressed size is 8.9 MB. This is totally crazy! There is really room for improvement here.
A lot of JavaScript often means you are downloading more than you need. How complex is the page and what can the user do on the page? Do you use multiple JavaScript frameworks?
privateAssetsThe page has 10 requests with private headers. Make sure that the assets really should be private and only used by one user. Otherwise, make it cacheable for everyone.
If you set private headers on content, that means that the content are specific for that user. Static content should be able to be cached and used by everyone. Avoid setting the cache header to private.
firstContentfulPaintFirst contentful paint can be improved (2.324 s). It is in the Google Web Vitals needs improvement range, slower than 1.8 seconds.
The First Contentful Paint (FCP) metric measures the time from when the page starts loading to when any part of the page content is rendered on the screen. For this metric, "content" refers to text, images (including background images), <svg> elements, or non-white <canvas> elements.
faviconThe favicon size is 15.6 kB bytes. That's quite big, can you make it smaller?
It is easy to make the favicon big but please avoid doing that, because every browser will then perform an unnecessarily large download. And make sure the cache headers are set for a long time for the favicon. It is easy to miss since it's another content type.
compressAssetsThe page has 3 requests that are served uncompressed. You could save a lot of bytes by sending them compressed instead.
In the early days of the Internet there were browsers that didn't support compressing (gzipping) text content. They do now. Make sure you compress HTML, JSON, JavaScript, CSS and SVG. It will save bytes for the user; making the page load faster and use less bandwith.
| URL | Transfer | Content |
|---|---|---|
| https://stripe.com/in | 186.7 KB | 679.8 KB |
| https://b.stripecdn.com/mkt-statics-srv/assets/imt-c080f20b4b766409cce89f224b019648.js | 18.2 KB | 81.2 KB |
| https://api.company-target.com/api/v3/ip.json...om/api/v3/ip.json | 2.8 KB | 2.3 KB |
cacheHeadersLongThe page has 20 requests that have a shorter cache time than one year (but still a cache time).
Setting a cache header is good. Setting a long cache header (a year) is even better because the asset will stay in the browser cache across visits. For content-hashed URLs (e.g. app.4af2.css) you can safely use Cache-Control: max-age=31536000, immutable. For unversioned URLs that may change, use a revalidating strategy instead.
fewFontsThe page has 2 font requests. Do you really need them? What value does the fonts give the user?
How many fonts do you need on a page for the user to get the message? Fonts can slow down the rendering of content, try to avoid loading too many of them because worst case it can make the text invisible until they are loaded (FOIT—flash of invisible text), best case they will flicker the text content when they arrive.
spofThe page has 5 requests inside of the head that can cause a SPOF (single point of failure). Load them asynchronously or move them outside of the document head.
A page can be stopped from loading in the browser if a single JavaScript, CSS, and in some cases a font, couldn't be fetched or is loading really slowly (the white screen of death). That is a scenario you really want to avoid. Never load 3rd-party components synchronously inside of the head tag.
optimalCssSizehttps://b.stripecdn.com/mkt-ssr-statics/assets/_next/static/css/f5d7a0708b41b5bf.css size is 40.4 kB (40437) and that is bigger than the limit of 25 kB. Try to keep each CSS response under 25 kB.
Render-blocking CSS holds up the first paint until it has fully downloaded, parsed and applied, so smaller CSS files mean a faster start. Split your CSS into a small critical bundle inlined or eagerly loaded, with the rest lazy-loaded.
| URL | Transfer | Content |
|---|---|---|
| https://b.stripecdn.com/mkt-ssr-statics/assets/_next/static/css/f5d7a0708b41b5bf.css | 39.5 KB | 296.4 KB |
modernImageFormatsThe page ships 2 images (out of 40) in JPEG/PNG/GIF without a modern alternative. Wrap them in a <picture> with a <source type="image/avif"> or "image/webp" before the legacy <img>, or serve modern formats from your image pipeline directly. AVIF and WebP usually deliver 25–50% smaller files at the same quality.
AVIF and WebP routinely deliver 25–50% smaller files than JPEG and PNG at the same perceived quality, and every browser version still under support understands at least one of them. Ship modern formats either through a <picture> element with <source type="image/avif"> / "image/webp" entries in front of the legacy <img>, or directly from a content-negotiating image pipeline that returns AVIF / WebP when the client accepts it. https://web.dev/articles/serve-images-webp
unnecessaryHeadersThere are 11 responses that sets a p3p header. There are 8 responses that sets both a max-age and expires header. There are 18 responses that sets a pragma no-cache header (that is a request header). There are 2 responses that sets a x-frame-options:sameorigin header. There are 161 responses that sets a server header.
Do not send headers that you don't need. We look for p3p, cache-control and max-age, pragma, server and x-frame-options headers. Have a look at Andrew Betts - Headers for Hackers talk as a guide https://www.youtube.com/watch?v=k92ZbrY815c or read https://www.fastly.com/blog/headers-we-dont-want.
thirdPartyThe page do 33% requests to third party domains (58 requests and 849 kB). First party is 117 requests and 1.9 MB. The regex .*stripe.* was used to calculate first/third party requests.
Do not load most of your content from third party URLs.
longHeadershttps://stripe.com/ has a header content-security-policy that is 1791 characters long. https://stripe.com/ has a header report-to that is 678 characters long. https://stripe.com/c.../enforcement-mode has a header content-security-policy that is 2212 characters long. https://stripe.com/c.../enforcement-mode has a header report-to that is 678 characters long. https://stripe.com/i.../in/notifications has a header content-security-policy that is 2212 characters long. https://stripe.com/i.../in/notifications has a header report-to that is 678 characters long. https://b.stripecdn....leTagManager.html has a header content-security-policy that is 1797 characters long. https://b.stripecdn....leTagManager.html has a header content-security-policy that is 1797 characters long. https://stripe.com/s...ttribution/imt.js has a header content-security-policy that is 2212 characters long. https://stripe.com/s...ttribution/imt.js has a header report-to that is 678 characters long. https://b.stripecdn....e89f224b019648.js has a header content-security-policy that is 2212 characters long. https://b.stripecdn....e89f224b019648.js has a header report-to that is 678 characters long. https://analytics.tw...ter.com/1/i/adsct has a header set-cookie that is 904 characters long. https://stripe.com/c.../enforcement-mode has a header content-security-policy that is 2212 characters long. https://stripe.com/c.../enforcement-mode has a header report-to that is 678 characters long. https://ad.doublecli...2Uf_nxeDg;epver=2 has a header location that is 1156 characters long. https://px.ads.linke...kedin.com/collect has a header set-cookie that is 718 characters long. https://px.ads.linke...edin.com/collect/ has a header set-cookie that is 811 characters long.
Do not send response headers that are too long.
iframeSandboxThe page embeds 4 cross-origin iframes without a sandbox attribute. Add sandbox="" with the minimum set of allow-* tokens the embed actually needs.
Adding a sandbox attribute to a cross-origin iframe restricts what the embedded page can do (script execution, form submission, top-level navigation, popups, etc.) and is one of the cheapest ways to limit the blast radius of a third-party embed. https://developer.mozilla.org/en-US/docs/Web/HTML/Element/iframe#sandbox
referrerPolicyNo <meta name="referrer"> tag was found on the page. Set a Referrer-Policy response header (preferred) or add a meta tag, for example <meta name="referrer" content="strict-origin-when-cross-origin">.
Without an explicit referrer policy the browser falls back to the user-agent default and may leak the full URL of the previous page (including query strings) to every cross-origin request. Set a Referrer-Policy response header (preferred) or a <meta name="referrer"> tag in the document. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Referrer-Policy
contentSecurityPolicyHeaderSet a Content-Security-Policy header to mitigate cross-site scripting attacks. You can start with a Content-Security-Policy-Report-Only header, which only reports violations rather than blocking them.
A Content-Security-Policy response header tells the browser which sources of script, style, and other content are allowed. The most effective form is a strict CSP using nonces or hashes together with strict-dynamic; the worst is a missing header, with unsafe-inline and unsafe-eval close behind. https://web.dev/articles/strict-csp
crossOriginEmbedderPolicyHeaderSet a Cross-Origin-Embedder-Policy header (typically require-corp or credentialless) on the document response to control cross-origin embedding.
Cross-Origin-Embedder-Policy (COEP) makes the page refuse to load cross-origin subresources unless they explicitly opt in via CORP or CORS. Together with Cross-Origin-Opener-Policy it puts the page in a cross-origin isolated context, which mitigates cross-window side-channel attacks (Spectre) and unlocks high-resolution timers and SharedArrayBuffer. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Embedder-Policy
crossOriginOpenerPolicyHeaderSet a Cross-Origin-Opener-Policy header (typically same-origin) on the document response to isolate the page from cross-origin windows.
Cross-Origin-Opener-Policy (COOP) lets a page sever its window-group ties to cross-origin documents that opened it or that it opens. Together with Cross-Origin-Embedder-Policy it puts the page in a cross-origin isolated context, which mitigates cross-window side-channel attacks (Spectre) and unlocks high-resolution timers and SharedArrayBuffer. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Opener-Policy
crossOriginResourcePolicyHeaderSet a Cross-Origin-Resource-Policy header (same-origin, same-site or cross-origin) on the document response to limit who may embed it.
Cross-Origin-Resource-Policy (CORP) is a per-response opt-in that tells the browser which origins are allowed to embed the resource. It blocks cross-origin or cross-site no-cors embedding (img, script, iframe, etc.) and is one of the building blocks of cross-origin isolation. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Resource-Policy
nelHeaderSet a NEL header (paired with Reporting-Endpoints) to collect connection-level error reports from the field.
The NEL (Network Error Logging) response header tells the browser to record connection-level failures (DNS, TLS, HTTP errors) and ship them to a reporting endpoint. NEL pairs with the Reporting-Endpoints / Report-To header — the page declares the endpoint group and NEL points at it. Together they give you visibility into errors that never reach your origin server. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/NEL
permissionsPolicyHeaderSet a Permissions-Policy header to control which browser features the page can use.
The Permissions-Policy response header (the successor to Feature-Policy) lets a site explicitly opt in or out of powerful browser features such as camera, microphone, geolocation, payment and clipboard. Setting a strict policy reduces the attack surface and limits what embedded third parties can do. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Permissions-Policy
referrerPolicyHeaderSet a referrer-policy header to make sure you do not leak user information.
Referrer Policy is a new header that allows a site to control how much information the browser includes with navigations away from a document and should be set by all sites. https://scotthelme.co.uk/a-new-security-header-referrer-policy/.
reportingEndpointsHeaderSet a Reporting-Endpoints header (or the legacy Report-To header) so CSP reports, NEL data and other Reporting-API events have an endpoint to land at.
The Reporting-Endpoints response header (the successor to Report-To) names the URLs that browsers should POST reports to. Without it, CSP report-to directives, Cross-Origin-Opener-Policy reports, NEL data and other Reporting-API events have nowhere to go. The legacy Report-To header is still accepted for older Chromium versions. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Reporting-Endpoints
thirdPartyCookiesThe page sets 11 third party cookies.
Third party cookies are used to track the user. They are automatically blocked in Safari and Firefox.
thirdPartyPrivacyThe page has 26% requests that are 3rd party (46 requests with a size of 821.9 kB). The page also have request to companies that harvest data from users and do not respect users privacy (see https://en.wikipedia.org/wiki/Surveillance_capitalism). The page do 5 tag-manager requests and uses 1 tag-manager tool. The page do 17 surveillance requests and uses 5 surveillance tools. The page do 5 analytics requests and uses 3 analytics tools. The page do 24 ad requests and uses 7 ad tools. The page do 5 social requests and uses 3 social tools. The page do 2 marketing requests and uses 1 marketing tool. The page do 5 utility requests and uses 1 utility tool.
Using third party requests shares user information with that third party. Please avoid that! The project https://github.com/patrickhulce/third-party-web is used to categorize first/third party requests.
xContentTypeOptionsHeaderSet X-Content-Type-Options: nosniff on the document response to prevent MIME-sniffing.
X-Content-Type-Options: nosniff prevents browsers from interpreting files as a different MIME type than what is declared in the Content-Type header. This blocks a class of cross-site scripting and content-type confusion attacks and should be set on every response. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Content-Type-Options
A snapshot of what the browser actually built for this page: the document, how big and deep the DOM tree is and what it kept in storage. Big, deep trees are slower to style and lay out, so the counts Chrome warns about carry a flag.
Document
What the page says it is and how large it rendered.
DOM structure
How much markup the browser has to build, style and lay out.
Storage and connection
What the page stored on the client, and the network it was tested on.
Data collected using
Coach-core version 9.2.1. With updated code from
Webappanalyzer 2026-05-04. Use
--browsertime.firefox.includeResponseBodies html or
--browsertime.chrome.includeResponseBodies html to help Wappalyzer find more information about technologies used.
Data collected using Third Party Web version 0.29.2.
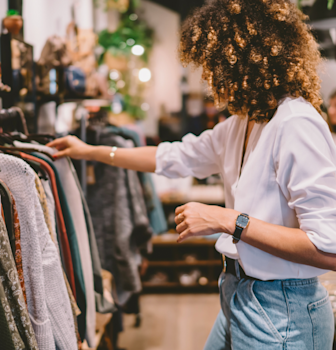
0.0s3.4s4.7s6.0s7.3s8.6s9.9s11.2sWhen the page main content is rendered, collected via the Largest Contentful Paint API. Read more about Largest Contentful Paint.
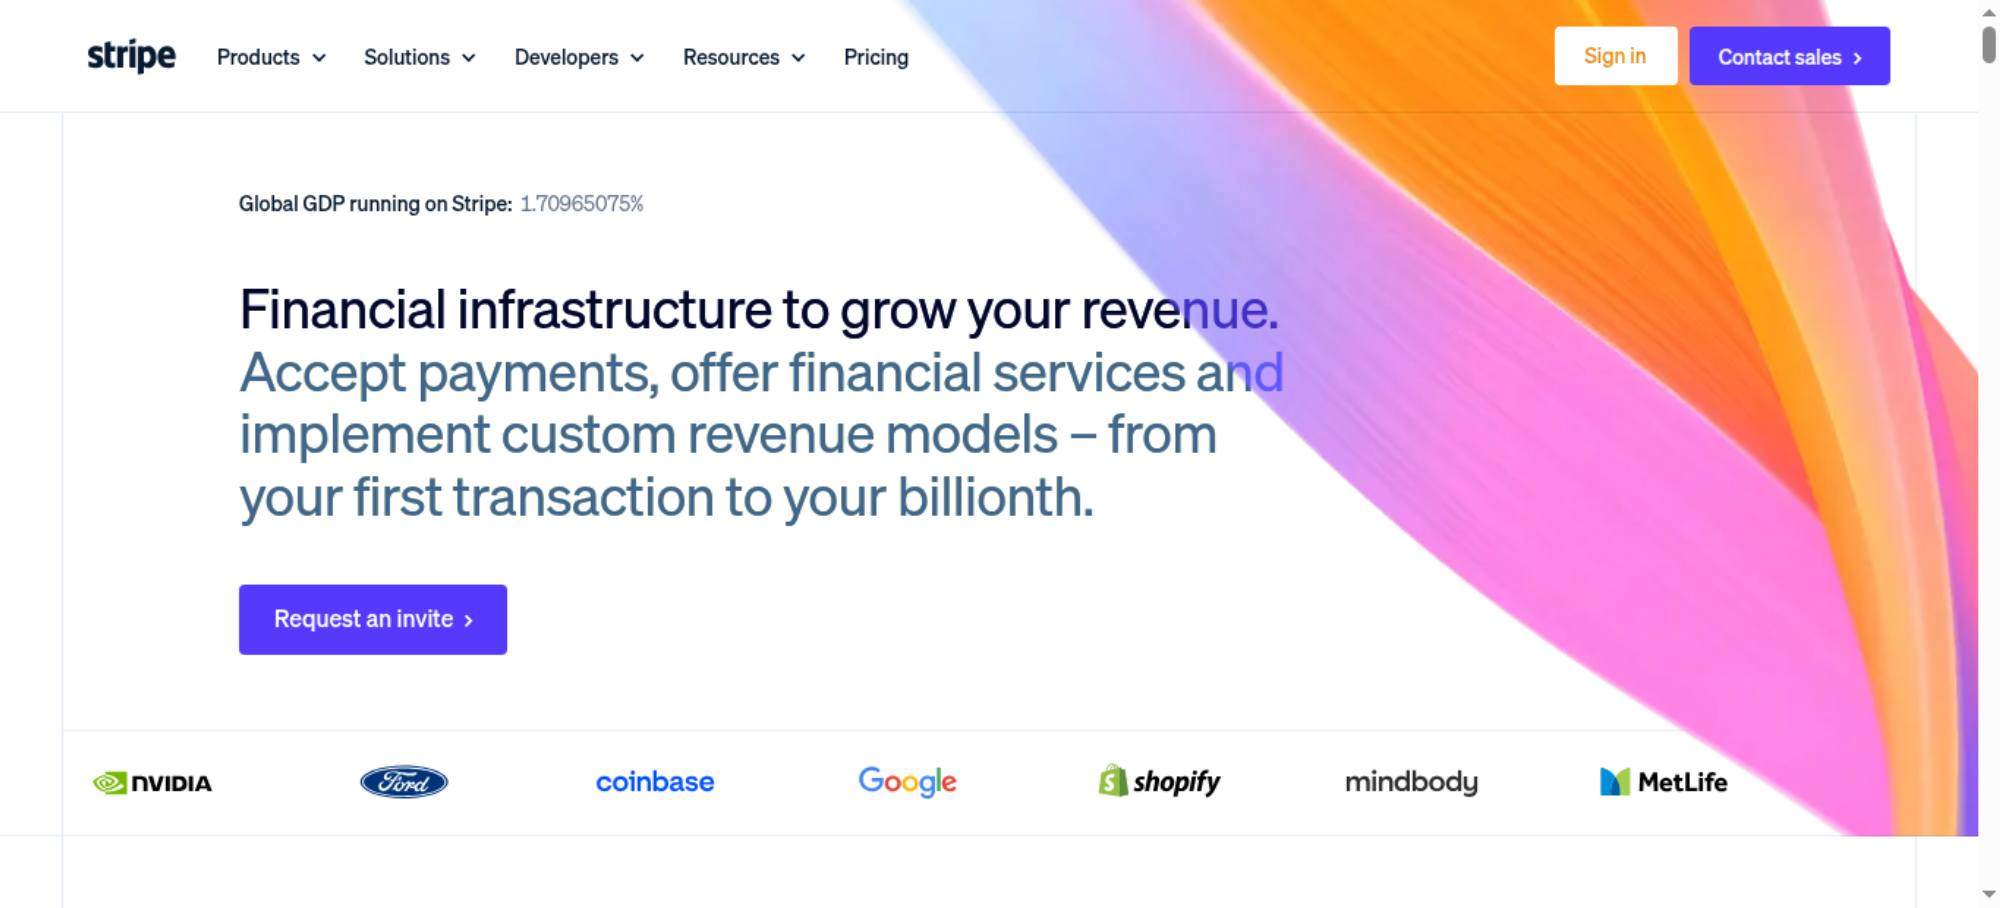
The LCP element is highlighted in the screenshot. If nothing is highlighted the element was removed before the screenshot or the LCP API couldn't find it.
The Largest Contentful Paint API matched this image:
How much the page's content shifts as it loads, collected via the Cumulative Layout Shift API.
No layout shifts were detected on this page.
There are no custom configured scripts.
There are no custom extra metrics from scripting.
How the page is built.
| Header | Value |
|---|---|
access-control-allow-credentials | true |
access-control-allow-headers | Content-Type |
access-control-allow-origin | https://m.stripe.network |
content-length | 138 |
content-type | text/html application/json;charset=utf-8 |
date | Fri, 04 Sep 2026 07:39:23 GMT |
location | https://stripe.com |
server | nginx |
strict-transport-security | max-age=31556926; includeSubDomains; preload |
Transfer size2.7 MB
Content size10.0 MB
Requests160
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 193.0 KB | 681.0 KB | 8 |
| css | 0 b | 63.9 KB | 467.1 KB | 5 |
| javascript | 496 B | 2.1 MB | 8.5 MB | 103 |
| image | 1.6 KB | 270.9 KB | 262.8 KB | 22 |
| font | 0 b | 70.2 KB | 69.1 KB | 2 |
| favicon | 0 b | 15.3 KB | 14.7 KB | 1 |
| json | 0 b | 12.5 KB | 2.9 KB | 7 |
| plain | 0 b | 1.5 KB | 0 b | 11 |
| other | 0 b | 0 b | 0 b | 1 |
| Total | 2.1 KB | 2.7 MB | 10.0 MB | 160 |
| Domain | Total download time | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| m.stripe.com | 1.127 s | N/A | 0 b | 1 |
| stripe.com | 2.159 s | 195.2 KB | 679.9 KB | 6 |
| b.stripecdn.com | 25.934 s | 1.4 MB | 6.0 MB | 94 |
| images.stripeassets.com | 653 ms | 265.8 KB | 262.3 KB | 9 |
| q.stripe.com | 2.895 s | 876 B | 86 B | 4 |
| r.stripe.com | 608 ms | N/A | 0 b | 2 |
| www.googletagmanager.com | 1.569 s | 662.3 KB | 2.5 MB | 5 |
| assets.stripeassets.com | 62 ms | 15.3 KB | 14.7 KB | 1 |
| munchkin.marketo.net | 148 ms | 4.1 KB | 9.2 KB | 1 |
| static.ads-twitter.com | 102 ms | 14.8 KB | 52.7 KB | 1 |
| www.redditstatic.com | 251 ms | 20.4 KB | 71.0 KB | 1 |
| snap.licdn.com | 217 ms | 41.4 KB | 115.6 KB | 2 |
| tag.flvcdn.net | 291 ms | 9.6 KB | 31.6 KB | 1 |
| s.yimg.jp | 669 ms | 11.8 KB | 35.5 KB | 1 |
| bat.bing.com | 999 ms | 16.3 KB | 54.4 KB | 3 |
| js.zi-scripts.com | 783 ms | 6.7 KB | 20.0 KB | 3 |
| tag.demandbase.com | 183 ms | 20.2 KB | 69.4 KB | 1 |
| d34r8q7sht0t9k.cloudfront.net | 137 ms | 6.8 KB | 13.6 KB | 1 |
| px.ads.linkedin.com | 2.140 s | 1.4 KB | 43 B | 5 |
| www.google.com | 1.860 s | 124 B | 84 B | 5 |
| www.facebook.com | 180 ms | 275 B | 0 b | 1 |
| b91.yahoo.co.jp | 804 ms | 62 B | 42 B | 1 |
| t.co | 450 ms | 668 B | 43 B | 1 |
| analytics.twitter.com | 404 ms | 1013 B | 43 B | 1 |
| match.adsrvr.org | 571 ms | N/A | 0 b | 2 |
| ipv4.pdscrb.com | 1.201 s | 225 B | 25 B | 1 |
| pixel-config.reddit.com | 104 ms | 236 B | 32 B | 1 |
| alb.reddit.com | 386 ms | 666 B | 42 B | 1 |
| id.rlcdn.com | 662 ms | N/A | 0 b | 2 |
| api.company-target.com | 229 ms | 2.8 KB | 2.3 KB | 1 |
| googleads.g.doubleclick.net | 161 ms | 3.2 KB | 6.6 KB | 1 |
| analytics.google.com | 363 ms | N/A | 0 b | 2 |
| stats.g.doubleclick.net | 194 ms | 549 B | 0 b | 1 |
| attr-td.ml-api.io | 492 ms | 340 B | 72 B | 1 |
| apm.yahoo.co.jp | 743 ms | 695 B | 43 B | 1 |
| tag-logger.demandbase.com | 873 ms | 418 B | 0 b | 1 |
| ws.zoominfo.com | 743 ms | 1.9 KB | 3.2 KB | 2 |
| ad.doubleclick.net | 656 ms | N/A | 0 b | 2 |
| segments.company-target.com | 503 ms | 287 B | 26 B | 2 |
| www.linkedin.com | 660 ms | N/A | 0 b | 2 |
| verifi.pdscrb.com | 1.223 s | 238 B | 42 B | 1 |
| type | min | median | max |
|---|---|---|---|
| Expires | 0 seconds | 1 year | 1 year |
| Last modified | 2 hours | 8 hours | 56 years |
Includes requests done after load event end.
| Content | Transfer Size | Requests |
|---|---|---|
| html | 418 B | 3 |
| css | 0 b | 0 |
| javascript | 657.6 KB | 19 |
| image | 4.8 KB | 12 |
| font | 0 b | 0 |
| favicon | 15.3 KB | 1 |
| plain | 1.5 KB | 10 |
| json | 6.9 KB | 5 |
| other | 0 b | 1 |
| Total | 686.6 KB | 64 |
Includes requests done after DOM content loaded.
| Content | Transfer Size | Requests |
|---|---|---|
| html | 6.3 KB | 7 |
| css | 0 b | 0 |
| javascript | 897.3 KB | 30 |
| image | 141.5 KB | 18 |
| font | 0 b | 0 |
| favicon | 15.3 KB | 1 |
| json | 12.5 KB | 7 |
| plain | 1.5 KB | 11 |
| other | 0 b | 1 |
| Total | 1.0 MB | 88 |
Third party requests categorised by Third party web version 0.29.2.
Requests by category63
Domains that didn't match any tool in Third party web. If you are sure they are third party domains, please do a PR to that project. You can also fine tune the list using --firstParty.
Transfer size2.7 MB
Content size10.0 MB
Requests175
Calculated using .*stripe.* (use --firstParty to configure).
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 192.5 KB | 681.0 KB | 5 |
| css | 0 b | 63.9 KB | 467.1 KB | 5 |
| javascript | 0 b | 1.3 MB | 5.5 MB | 83 |
| image | 0 b | 266.4 KB | 262.4 KB | 11 |
| font | 0 b | 70.2 KB | 69.1 KB | 2 |
| favicon | 0 b | 15.3 KB | 14.7 KB | 1 |
| json | 0 b | 8.5 KB | 32 B | 3 |
| plain | 0 b | 305 B | 0 b | 4 |
| Total | N/A | 1.9 MB | 7.0 MB | 117 |
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 418 B | 0 b | 3 |
| css | 0 b | 0 b | 0 b | 0 |
| javascript | 496 B | 818.8 KB | 3.0 MB | 20 |
| image | 1.6 KB | 4.5 KB | 480 B | 11 |
| font | 0 b | 0 b | 0 b | 0 |
| favicon | 0 b | 0 b | 0 b | 0 |
| plain | 0 b | 1.2 KB | 0 b | 7 |
| json | 0 b | 4.0 KB | 2.9 KB | 4 |
| other | 0 b | 0 b | 0 b | 1 |
| Total | 2.5 KB | 829.1 KB | 3.0 MB | 58 |